
Bhubaneswar (By Santosh Kumar): A series of viral videos involving the BAT-BMS mobile application has sparked widespread concern over the cybersecurity of Battery Management Systems (BMS) used in electric vehicles across India, particularly commercial e-rickshaws. The videos, which have gained significant traction on social media platforms, appear to show individuals using Bluetooth-enabled diagnostic applications to connect to nearby battery systems, allegedly causing vehicles to stop unexpectedly.
The incidents have prompted discussions among e-rickshaw drivers, fleet operators, battery manufacturers, cybersecurity researchers, and government agencies about the security of Bluetooth-enabled Battery Management Systems and the broader cybersecurity challenges facing India’s rapidly expanding electric mobility ecosystem.
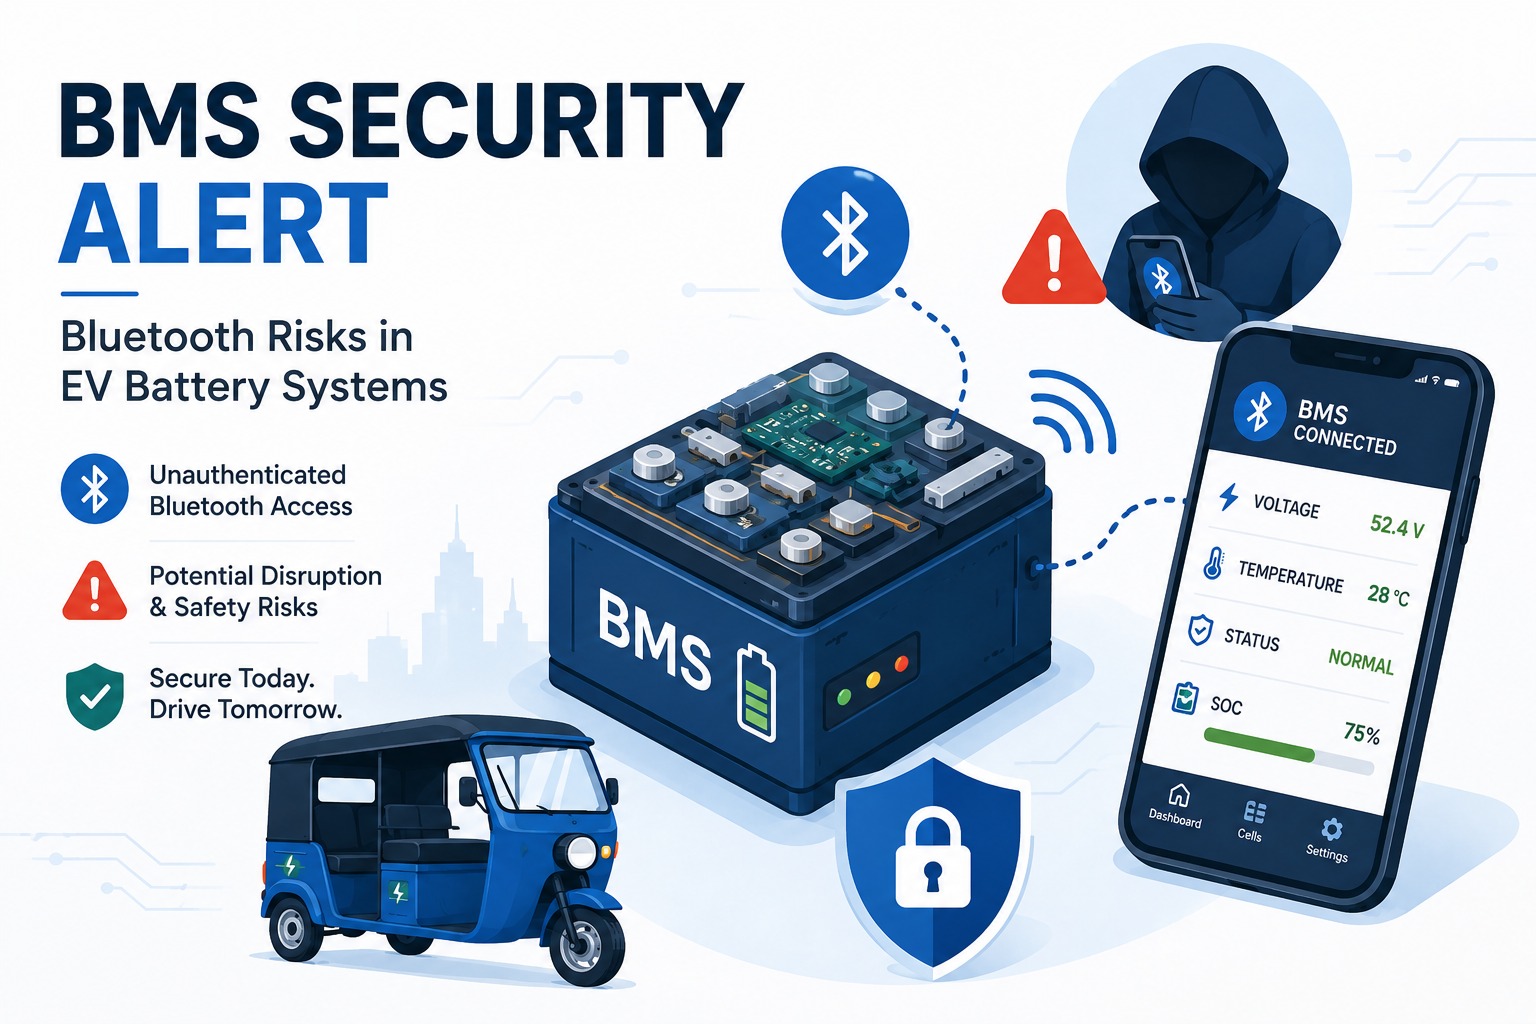
According to multiple media reports, the issue appears to involve certain Battery Management Systems that expose Bluetooth Low Energy (BLE) interfaces without adequate authentication or continue operating with factory-default credentials. In such cases, an unauthorized person within Bluetooth range may be able to establish a connection using compatible diagnostic applications if the battery has not been securely configured.
Cybersecurity experts note that the issue is not related to malware, ransomware, or internet-based remote hacking. Instead, it involves local Bluetooth communication with vulnerable Battery Management Systems that lack sufficient authentication and access control mechanisms. The reported behavior depends on the specific battery hardware, firmware, and security configuration, meaning it does not affect every electric vehicle or every Battery Management System currently in use.
TraceX Labs Publishes Comprehensive Technical Advisory
Following an independent technical assessment of the reported incidents, TraceX Labs has released a comprehensive cybersecurity advisory titled:
“Unauthorized Over-the-Air Disruption of EV Battery Management Systems (BMS) via Unauthenticated Bluetooth Low Energy (BLE) Controls.”
Prepared by the TraceX Labs IoT Security Research Team, the advisory provides an in-depth technical analysis of the reported security issue, examines how insecure Bluetooth implementations may expose critical battery control functions, and outlines practical mitigation measures for battery manufacturers, EV manufacturers, fleet operators, commercial e-rickshaw drivers, service technicians, and regulatory authorities.
According to the advisory, the issue originates from insecure Bluetooth configurations rather than sophisticated cyber intrusion techniques. The report identifies several security weaknesses that may be present in affected Battery Management Systems, including missing authentication for critical Bluetooth functions, factory-default Bluetooth PINs, unrestricted access to battery control parameters, the absence of access control or device whitelisting, and Bluetooth interfaces that remain publicly discoverable after deployment.
When these conditions exist simultaneously, compatible Bluetooth diagnostic applications may be capable of communicating with vulnerable Battery Management Systems without appropriate authorization.
Potential Impact on India’s Electric Mobility Sector..
Battery Management Systems are responsible for monitoring and protecting lithium-ion battery packs by managing charging, discharging, cell balancing, voltage regulation, and temperature protection.
The TraceX Labs advisory explains that if unauthorized users gain access to sensitive battery controls on vulnerable systems, it could potentially interrupt normal battery operation, creating operational and public safety concerns for electric vehicles in service.
The advisory identifies several potential risks, including:
Unexpected interruption of vehicle operation.
Increased road safety risks for drivers and passengers.
Operational disruption for commercial fleet operators.
Financial losses resulting from vehicle downtime.
Reduced public confidence in connected electric mobility technologies.
The report further notes that India’s rapidly expanding electric mobility sector, combined with the widespread deployment of Bluetooth-enabled Battery Management Systems supplied through diverse manufacturing and assembly chains, makes cybersecurity an increasingly important consideration across the EV ecosystem.
Immediate Mitigation Recommendations..
To reduce potential exposure, TraceX Labs recommends that manufacturers, fleet operators, battery assemblers, service centers, and vehicle owners review the security configuration of Bluetooth-enabled Battery Management Systems without delay.
The advisory recommends:
Replacing factory-default Bluetooth passwords with strong, unique credentials.
Disabling Bluetooth advertising when wireless monitoring is unnecessary.
Restricting Bluetooth access to authorized maintenance personnel only.
Installing manufacturer-issued firmware updates where available.
Conducting security audits of deployed Battery Management Systems.
Temporarily disconnecting external Bluetooth communication modules where secure configuration is unavailable and wireless functionality is not required.
For Battery Management Systems that do not support password changes or secure Bluetooth configuration, the advisory also documents a temporary hardware mitigation procedure that isolates the Bluetooth communication module while preserving the battery’s core protection and management functions. TraceX Labs advises that any hardware modifications should only be performed by qualified technicians following appropriate electrical safety practices.
Long-Term Security Recommendations..
The advisory also encourages Battery Management System manufacturers to adopt secure-by-design principles in future products, including mandatory authentication, encrypted Bluetooth communications, secure pairing procedures, cryptographic verification of commands, secure firmware update mechanisms, and Bluetooth functionality disabled by default until securely configured.
In addition, TraceX Labs recommends strengthening automotive cybersecurity standards by incorporating mandatory wireless security testing, secure default configurations, and coordinated vulnerability disclosure practices into future regulatory requirements.
Complete Technical Advisory Available..
The complete TraceX Labs advisory includes a detailed Executive Summary, Technical Threat Analysis, Bluetooth Attack Methodology, India EV Ecosystem Risk Assessment, Hardware Mitigation Procedures, Software Security Guidance, Manufacturer Recommendations, Regulatory and Policy Recommendations, Supply Chain Vulnerability Assessment, and a Long-Term Cybersecurity Framework.
As India’s electric mobility sector continues to grow, the report concludes that cybersecurity must become a fundamental component of Battery Management System design and deployment. By implementing stronger authentication, secure communication protocols, and security-by-default practices, manufacturers and operators can significantly reduce the risks associated with connected battery technologies while improving the overall resilience of the country’s EV ecosystem.